Security & Compliance · ISO governance

Formal security before the client
asks for it, not at the
last minute.

A formal security governance program: ISO 27001 / 27002 / 42001, with evidence organized in PSA (Professional Services Automation). When the questionnaire arrives, you answer in days, not in months of panic.

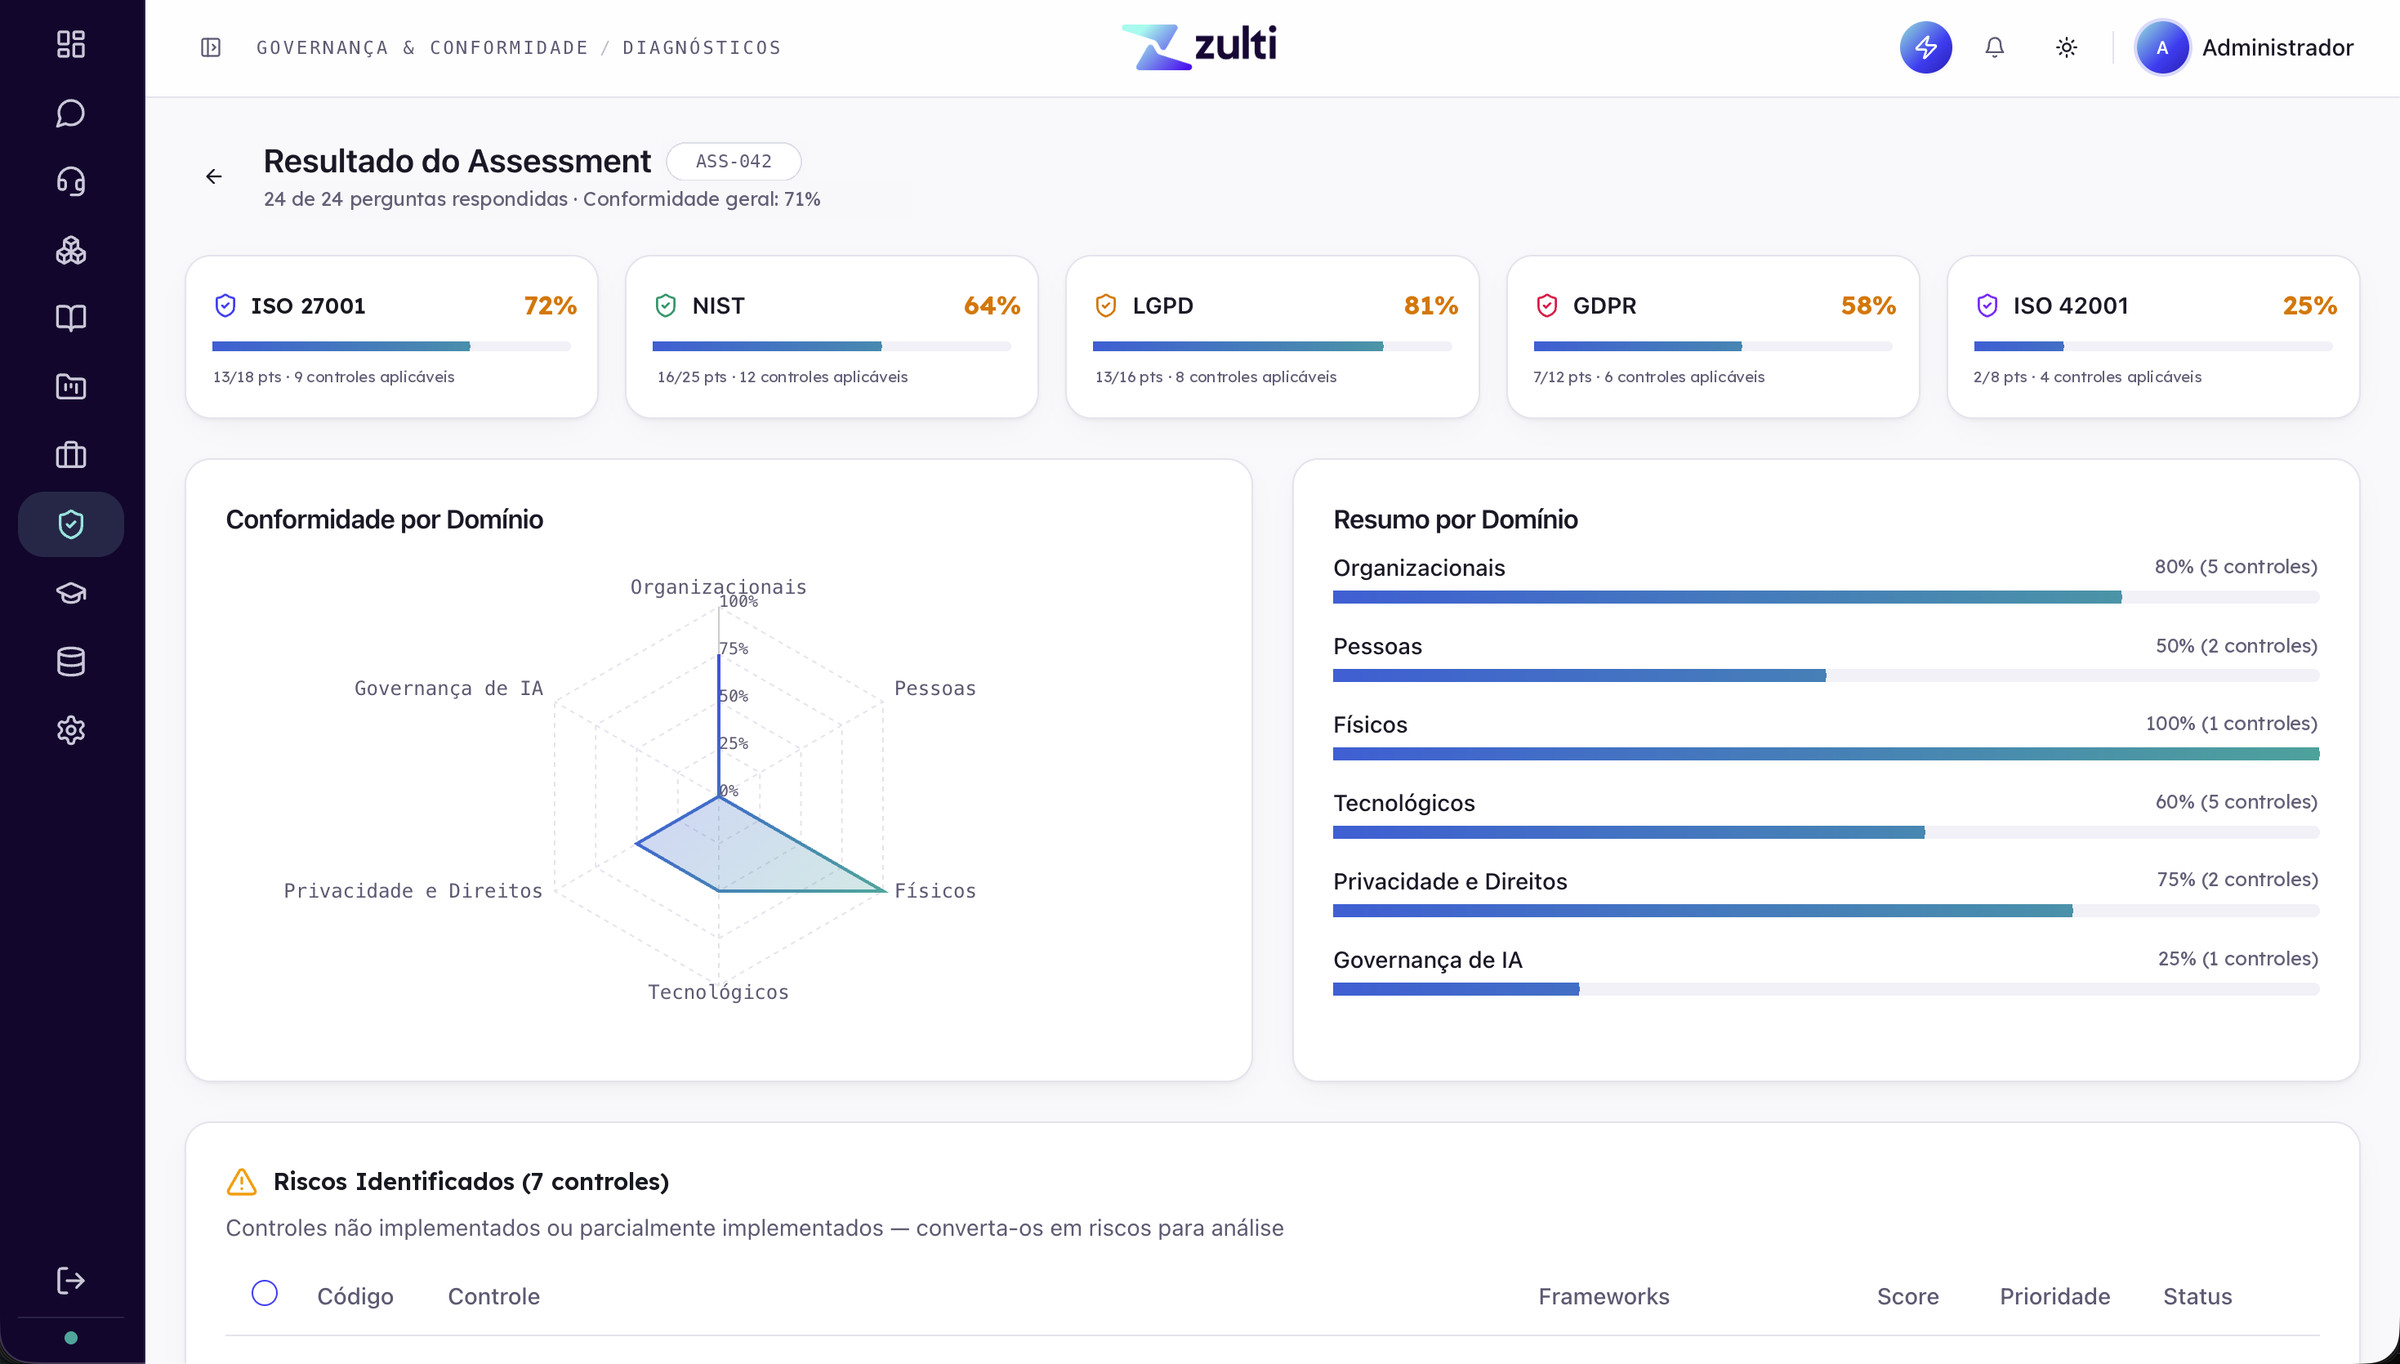
PSA · Assessment · ISO 27001 · NIST · LGPD · GDPR · ISO 42001
Assessment result in PSA: compliance by framework and domain, identified risks
model
project + retainer
standards
ISO 27001 + LGPD
delivery
dossier in PSA
Before the request arrives

You don't choose when you'll be asked. You only choose whether you'll be ready when it comes.

A Tier-1 client sends a questionnaire with a 15-day deadline. An investor opens due diligence. An auditor arrives with a fixed schedule. When the pressure comes, rushing is expensive: weak evidence, improvised policies, controls nobody has tested. The program needs to be in place before the pressure, not during it. It applies to companies of any size that don't yet have a formal security program, from those building one for the first time to large companies with low maturity that need to answer a client, an investor or an auditor.

The program's 4 areas

From assessment to a ready dossier.

Each area delivers part of the program, organized in PSA. Together, they let the company answer in days what would otherwise take weeks of rushing.

— Area 01

Posture assessment

Gap analysis against ISO 27001 (with LGPD integrated). Where the company is today vs where it needs to be, the basis for directing the program.

Non-conformity map
Security strategic plan (2–3 years, priorities)
Documented baseline
— Area 02

Documentation program

The security strategic plan (PESI) grounded in written policies, documented controls and an IT acceptable use policy: direction that becomes documents, and documents that become routine.

8–12 policies (InfoSec, Access, Backup, Incident)
14+ documented controls
IT acceptable use policy
— Area 03

Evidence in PSA

Zulti's own GRC platform. Zulti operates it, the client has read-only access, with evidence synced and always ready.

PSA configured + ISO domains
Logs, records and signatures synced
Client has read-only access to the program
— Area 04

Readiness for requests

When the request comes (a questionnaire, due diligence or an auditor), Zulti builds the response from PSA.

Questionnaire answered in days
Due diligence dossier assembled
Package for internal/external auditors
— Working alongside your in-house team
Zulti builds and directs; the client's in-house team runs the program day to day. Policies are written by Zulti but distributed and enforced by people inside the company. Evidence is organized in PSA by Zulti, but fed by the in-house team (logs, records, receipts). No competition with in-house IT, HR or legal: separate roles, agreed at onboarding.
separate roles · agreed at onboarding
How it's put together

A fixed project to build it. An optional retainer to keep it alive.

The program fits in a fixed project, weeks, not years. Assessment, documentation and an initial dossier in PSA, delivered with a defined scope and timeline. The retainer only makes sense when you want to keep the program up to date between audits, without rebuilding everything in a rush. And Zulti tells you upfront whether you fit this model or not.

— option 01

Fixed project

assessment + initial build-out

duration~12 weeks
deliveryfixed scope
billingsingle price
what's included
  • Posture assessment against ISO 27001 (LGPD integrated)
  • The security strategic plan (PESI) — Information Security Strategic Plan with 2–3 year priorities
  • A set of documented policies, controls and procedures
  • IT acceptable use policy for employees (HR attaches it to the employment contract)
  • Evidence organized in PSA, a dossier ready to hand over
  • Baseline training for leadership and process owners
  • Readiness letter for questionnaires / due diligence / auditors
makes sense when

You need to be ready for a known request (a Tier-1 client closing, a funding round in talks, a set audit calendar) and want to close the chapter with the program in place and no open-ended contract afterwards.

optional continuity — option 02

Project + retainer

build-out + ongoing upkeep

duration12 wks + monthly
deliveryfixed + recurring
billingone-off + fee
what's included beyond the project
  • PSA kept alive, evidence updated month by month
  • Annual review of the The security strategic plan (PESI) as the business changes
  • Policy reviews as the program matures
  • Answers to new questionnaires and due diligence during the year
  • Assessment of critical vendors in new contracts
  • Preparation for recertification or the annual audit
  • Written opinions on demand for security decisions
makes sense when

You serve clients who ask for annual revalidation, are entering a recurring audit cycle, or want to keep the program alive without restarting a project every time something changes in the business.

Build-out ≠ Execution

Zulti documents. You choose who implements.

S&C delivers the documentation program and the dossier in PSA: formalized policies, controls and procedures. Tightening the technical screws in the environment (hardening, MFA, segregation, backup, monitoring) is a separate step. Zulti doesn't force it: you decide who executes.

option 01

Your in-house IT

Zulti documents, trains process owners and validates the implementation at the end of each cycle. It works when the in-house team has the technical skills to execute.

option 02

Zulti MSP (separate contract)

When you prefer to outsource execution, Zulti's MSP takes what was documented and implements it in the environment. Same company, separate contract, no forced bundle.

option 03

Another provider

You already work with an MSP you'd like to keep, or want to get quotes. The documentation program stands on its own: any competent provider can execute from the written policies.

Project cost rises with urgency. A program built on its own calendar takes 8–12 weeks and fits the team's routine. A program built after the client has asked, on a short deadline, turns into late nights, a squeezed scope, rework and a real risk that the auditor won't accept evidence produced in a hurry.

Featured case · S&C in action

When a Big Tech audit came in,
Álamo passed with 100%.

A marketing agency partnered with a Big Tech company had to comply with that partner's The security strategic plan (PESI) (information security strategic plan) and align its environment with ISO 27001 / 27002 and LGPD to keep the contract. Zulti built the program before the deadline got tight (assessment, security plan, policies, controls and evidence) and took the company into the audit with no improvising. Result: 100% adherence, contract kept.

Operational compliance, not a checklist. Always audit-ready.
Book a call →
Frequently asked questions

When compliance is required, every CEO asks the same things.

What's truly auditable, what's theater, and what holds up day to day.

How does the fixed project work? How long until the program is ready?+
~12 weeks, three blocks. Assessment (weeks 1–3): gap analysis against ISO 27001 with LGPD integrated + a security strategic plan with 2–3 year direction. Build-out (4–9): policies, controls and an IT acceptable use policy, written for that client, not a template. Loading into PSA (10–12): organized evidence, a dossier and a readiness letter for questionnaires, due diligence or auditors. The contract ends there; the retainer is optional to keep the program alive between audits.
Do you issue the ISO 27001 certificate, or do I need an external auditor?+
An external auditor, always. An ISO 27001 certificate can only be issued by an accredited certification body (BSI, Bureau Veritas, DNV...). That's an accreditation rule (INMETRO/IAF), not a commercial choice. Zulti handles everything in between: it builds the program, organizes the evidence and gets the company ready to go into the audit without improvising. You hire the certification audit directly from the accredited body. If you only need to answer a client request (Tier-1, M&A), the program works without the certificate, which is the most common case.
Is the monthly retainer mandatory after the project?+
No. The fixed project ends with the deliverable: a documented program, a dossier in PSA, training delivered. The retainer only makes sense to keep the program alive: updated evidence, policy reviews as the business changes, answers to new questionnaires, recertification prep. A company serving a single Tier-1 client in one cycle may not need it; one with a recurring audit flow usually does. Zulti tells you upfront what makes sense for your case.
What's the difference between Security & Compliance and LGPD Compliance?+
Different scope and trigger. S&C builds the integrated program, ISO 27001 + LGPD together, starting from pressure by a client, investor or auditor asking for a broad security posture. When the trigger is LGPD only (the ANPD, a data subject requesting access, mapping after an incident), LGPD Compliance covers it: DPO, DPIA, mapping, ANPD. The paths cross, but S&C starts from broad governance and LGPD starts from personal data. Whoever needs both gets both, without paying for the same evidence twice.
PSA belongs to Zulti. If I end the contract, do I lose the dossier? Can I export it?+
You export everything. PSA is Zulti's own platform (operations + governance), run by us, with read-only access for the client during the contract. But the content (policies, controls, evidence, records) is yours: by contract, on termination you get a full export in an open format (PDF + structured ZIP, JSON for metadata), ready to load into any other GRC tool or keep on a corporate drive. No lock-in. That's not goodwill, it's a contract clause. PSA exists to organize, not to trap you.
Who it's NOT for

A compliance program isn't a certificate on the wall.

Commercial honesty has kept us going for almost a decade. In some scenarios, another model is a better fit. We list them openly to save you evaluation time.

✕
Your company doesn't yet have a defined internal sponsor for the program: who answers for security, who approves policies, who sits on the committee. Zulti builds programs that need an owner to run; if nobody inside is available to sign policies and push implementation, the program stands but doesn't move.
✕
You want an opinion to justify a decision already made, a commissioned "validation" to cover an internal choice of vendor or posture. Zulti gives an honest reading of your posture; when the recommendation goes against the client's preferred decision, it stands anyway. If the goal is a rubber stamp, this model creates friction.
✕
Your headquarters already has a corporate security program and you just want to replicate it locally without adapting it. Zulti doesn't do carbon copies: a program adapted to local reality (Brazilian vendors, CLT employment contracts, the ANPD instead of a foreign regulator) requires a fresh reading. When headquarters already provides the full formal structure and the local office only needs to execute, an MSP that follows headquarters' standards is a better fit.
More from Zulti

Services designed to cover every aspect of your IT.

Next step

Compliance can't be improvised when it's requested. We build it beforehand.

A direct 15-minute conversation. No off-the-shelf package, no forty-page proposal. The person you talk to makes the decisions.

or if you prefer
or tell us briefly